Sustainability Data Governance & Internal Control Audit
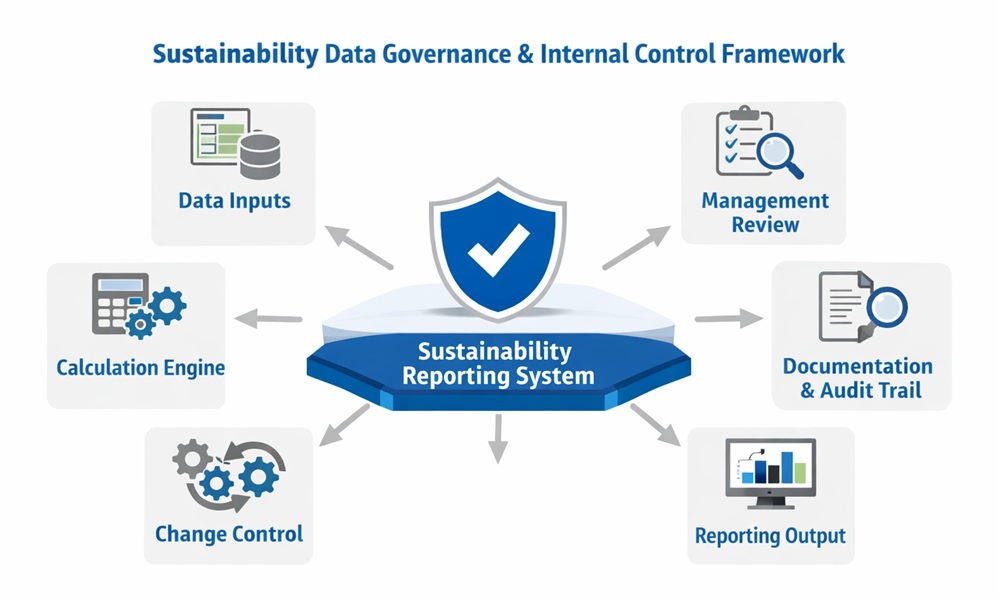
This engagement covers only the independent pre-submission audit and internal control assessment of your existing sustainability reporting systems and data governance framework.
Where DEISO provides sustainability execution services, system implementation, inventory development, or reporting support, such services are contracted separately and are not performed on the control environment subject to this independent review.
Sustainability data governance and internal control audit
Independent assessment of the control environment behind your ESG and GHG reporting — before external assurance sees it.Enterprise sustainability reporting increasingly depends on the integrity of data systems, emission controls, and governance architecture. Weak internal controls create defensibility risk during assurance engagement, procurement qualification, investor scrutiny, or regulatory escalation.
This engagement provides independent pre-submission audit of sustainability data governance and internal control environments across ESG and GHG reporting systems — without DEISO acting as a verification body or issuing verification statements.
Sustainability data governance control domains evaluated
| Control domain | Audit focus |
|---|---|
| Data input controls | Validation logic, supplier inputs, documentation completeness, data consistency checks |
| Calculation controls | Formula integrity, emission factor governance, version management, recalculation policy |
| Management review controls | Approval checkpoints, supervisory review evidence, escalation procedures |
| Documentation & audit trail | Evidence traceability, file control, record retention, transparency logic |
| Change control governance | Model updates, factor changes, structural modifications, authorization workflows |
| Reporting infrastructure | System architecture integrity, integration consistency, reporting output controls |
How the engagement runs
Governance scope definition
Define:
- Reporting frameworks in scope (ESG, GHG, Scope 1–3, PCF where applicable)
- Organizational boundary and reporting perimeter
- Sustainability data system architecture and calculation environments
- Control ownership structure and approval workflows
- Documentation maturity and audit trail completeness
- Risk exposure context (assurance, procurement, investor, regulatory)
Control environment audit execution
Structured pre-submission audit procedures evaluate governance consistency, data input controls, calculation integrity, emission factor governance, change management logic, and documentation traceability across the sustainability reporting infrastructure.
This includes control design assessment, version control evaluation, recalculation policy review, supervisory oversight testing, and evidence sampling to validate defensibility under structured external scrutiny.
Governance findings and reinforcement roadmap
You receive:
- Independent technical findings report
- Control maturity observations
- Identified governance or documentation gaps
- Risk-prioritized improvement recommendations
- Pre-submission readiness reinforcement guidance
Why DEISO for this work
- Carbon and ESG governance specialization
- Industrial-scale reporting architecture experience
- Control-first audit methodology aligned with assurance logic
- Risk-aware assessment focused on enterprise defensibility
- Independent, technically grounded governance review
We operate with discipline, documentation rigor, and governance sensitivity appropriate for enterprise sustainability systems.
Request a governance scope assessment
If your organization has established sustainability reporting systems and requires independent internal control evaluation prior to external assurance, procurement qualification, or regulatory review:
Request a confidential data governance assessment.
A structured scoping discussion determines:
- Frameworks and reporting systems in scope
- Control environment maturity level
- Data system complexity and integration depth
- Required audit depth and defensibility reinforcement level
- Estimated timeline and engagement structure
Submit a data governance audit inquiry
For enterprise sustainability data governance and internal control review engagements, submit a structured request to initiate a confidential reporting infrastructure and control maturity assessment.
Share this:
- Email a link to a friend (Opens in new window) Email
- Share on LinkedIn (Opens in new window) LinkedIn
- Share on X (Opens in new window) X
- Share on Facebook (Opens in new window) Facebook
- Share on WhatsApp (Opens in new window) WhatsApp
- Share on Reddit (Opens in new window) Reddit
- Print (Opens in new window) Print
- More